ABOUT CYVELLE
Enterprise Audit and Governance Experience, Applied to Your Next Decision.
We provide expert-led cybersecurity, audit readiness and AI governance support for growing businesses. The work starts with your requirement, reviews the evidence and turns gaps into accountable next steps.
01
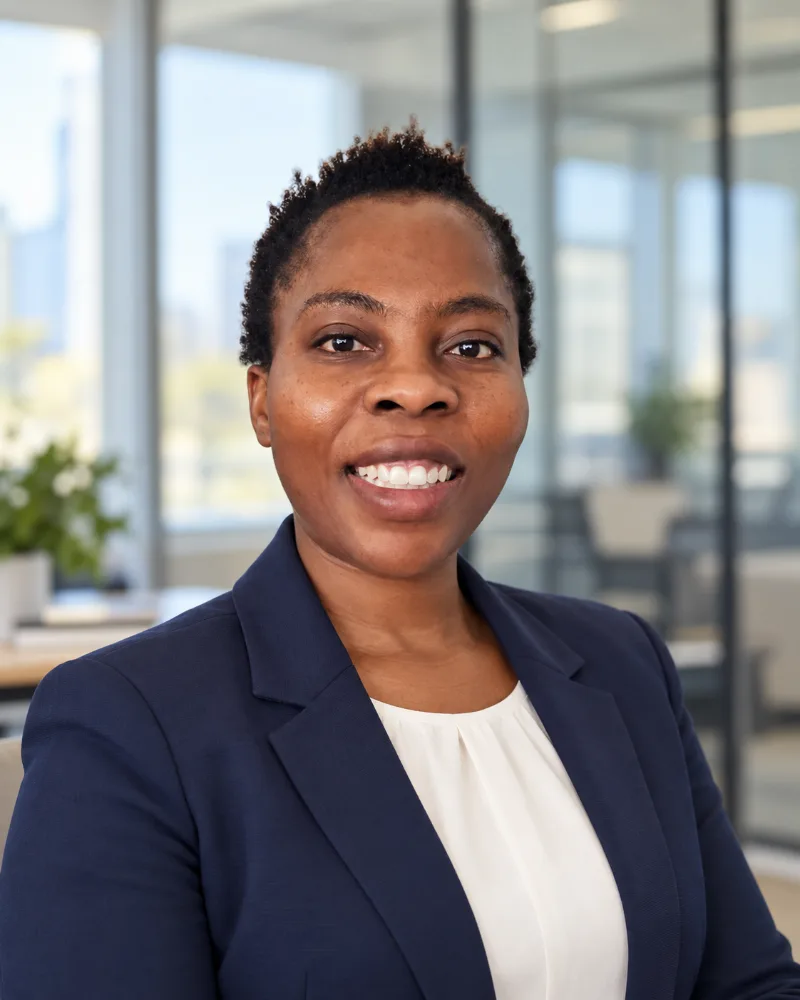
Meet Temi
Every Cyvelle engagement is led by Temi, bringing over two decades of consulting and enterprise experience in cybersecurity, IT audit, risk management, and compliance.
Her experience includes consulting engagements involving Fortune 100 organizations such as Amazon, IBM, Walgreens, and Humana, alongside professional experience at BDO and across financial services, healthcare, technology, and payments.
Today, she brings that enterprise-level experience directly to growing organizations, helping them identify security weaknesses, prepare for audits and certifications, and build practical compliance programs.
LinkedIn recommendations
Recommendations for Temi
Temi is an incredibly thorough GRC professional with an impressive command of PCI requirements. During our time working together, I was consistently impressed by her ability to navigate complex audit workflows and provide clear, actionable insights. She is a dedicated expert who brings high standards of professionalism to every project.
I’ve had the privilege of working alongside Temi, and I can confidently say she is one of the most reliable and technically proficient GRC and IT Security professionals I have partnered with. Her expertise spans SOX compliance, IT risk management, security controls, and governance frameworks, and she consistently brings clarity, structure, and rigor to every engagement.
Temi has a rare ability to translate complex regulatory requirements into practical, actionable controls that strengthen organizational resilience. Her attention to detail, strong analytical mindset, and commitment to high-quality execution make her an invaluable asset to any team. Beyond her technical strengths, she is collaborative, solutions-oriented, and trusted by stakeholders across the business.
Temi is GRC professional who has exhibited top level IT security risk and audit competence by leading high visibility, high impact projects building frameworks and implementation of systems that have improved the safety and reliability of business operations in global organizations. I have interacted with Temi on tangential projects and I can attest to her professionalism, commitment and leadership.
I had the privilege of being mentored by Temi during my transition from a general tech role into the security field, and I can confidently say her guidance made a significant difference in my journey.
Temi has a rare ability to support and uplift others in whatever capacity she can. She helped me not only understand complex security concepts and frameworks, but also gain practical, real-world exposure to the role. She taught me how to think like a security professional - from communicating security concepts to cross-functional teams with varying levels of understanding, to reviewing and analyzing security documentation for accuracy and completeness.
What stood out most was her genuine investment in my growth. Whether it was recommending resources, connecting me with a trainer to deepen my knowledge, reviewing my learning path, or sharing valuable industry insights, she was always generous with her time and expertise.
If you’re looking for a mentor or security leader who truly empowers others, I highly recommend Temi. I’m incredibly grateful for her support and the lasting impact she has had on my career.
Recommendations as published on LinkedIn, shown with the recommender's name and headline at the time of writing.
02
Professional credentials
- CISA
- CISM
- CRISC
- CDPSE
- PCI-QSA
- PCIP
Professional credentials belong to Temi. They do not make us an independent CPA firm, ISO certification body or HITRUST assessment organization.
03
Selected professional experience
The following examples describe Temi's professional experience rather than Cyvelle customer engagements.
| Area | Experience |
|---|---|
| SOC 2 Readiness | Led SOC readiness assessments for multiple clients, including a technology client that achieved four consecutive SOC reports with zero audit exceptions. |
| HITRUST | Built a security and compliance program from the ground up, achieving HITRUST certification in approximately six months and supporting a $50 million client contract. |
| PCI DSS Assessments | Led PCI DSS assessments for a technology client that achieved three consecutive clean Reports on Compliance (ROC) and Attestations of Compliance (AOC). |
| Security & Compliance Gap Assessments | Led security and compliance gap assessments across multiple frameworks, identifying control weaknesses, evaluating evidence, and developing prioritized remediation plans to strengthen security and audit readiness. |
Independent assurance providers issue their own reports and certificates. Past professional results do not guarantee a future engagement outcome.
04
How the work is approached
Direct expert leadership. Your scope and priorities are discussed with Temi. Responsibilities and deliverables are recorded before work begins.
Evidence before assertion. Findings identify what was reviewed, what the evidence supports and where limitations remain.
Connected requirements. Overlapping control requirements are mapped to reduce repeated requests while preserving framework-specific evidence needs.
Actions with ownership. The roadmap records priorities, proposed owners, dependencies and closure evidence. A finding without an owner remains visible governance work.
05
What to clarify before an engagement
A useful scope makes the buying decision clear as well as the work. Before agreeing an engagement, use these questions to confirm expectations.
Scope and evidence. Which business requirement, systems and frameworks are covered? What evidence will be reviewed, and how will unavailable or incomplete evidence be identified?
Responsibilities and dependencies. Who supplies information, approves decisions and owns follow-up actions? Which activities require your technical team, another specialist or an independent assurance provider?
Timing and review. What milestones are proposed, what could affect them, and how will you review the deliverables or request a scope change?
Fees and terms. What is the fee basis, when are payments due, and what do the agreed terms say about support, changes and cancellation?
Recommendation basis. What evidence and business needs support a recommendation, and are any relevant supplier relationships or incentives disclosed?
These questions help you compare a proposed engagement with the decision you need to make. Bring your deadline and any customer or contract requirements to the consultation.
06
Who Cyvelle serves
Startups responding to their first enterprise security review; small businesses facing questionnaires and contract requirements; growing companies coordinating several frameworks; and mid-market organizations improving governance across systems, suppliers and business units.
07
Choose a starting point
| Need | Route |
|---|---|
| Understand broader security/governance gaps | The Governance Blueprint → |
| Prepare for independent assessment | Compliance & Audit Readiness → |
| Establish ongoing security leadership | Virtual CISO → |
| Govern AI activities and responsibilities | AI Governance & Responsible AI → |
08
Work with the experience behind the advice
Bring the customer request, deadline or governance decision. We will discuss a useful starting scope.
Free 30-minute consultation. No obligation.